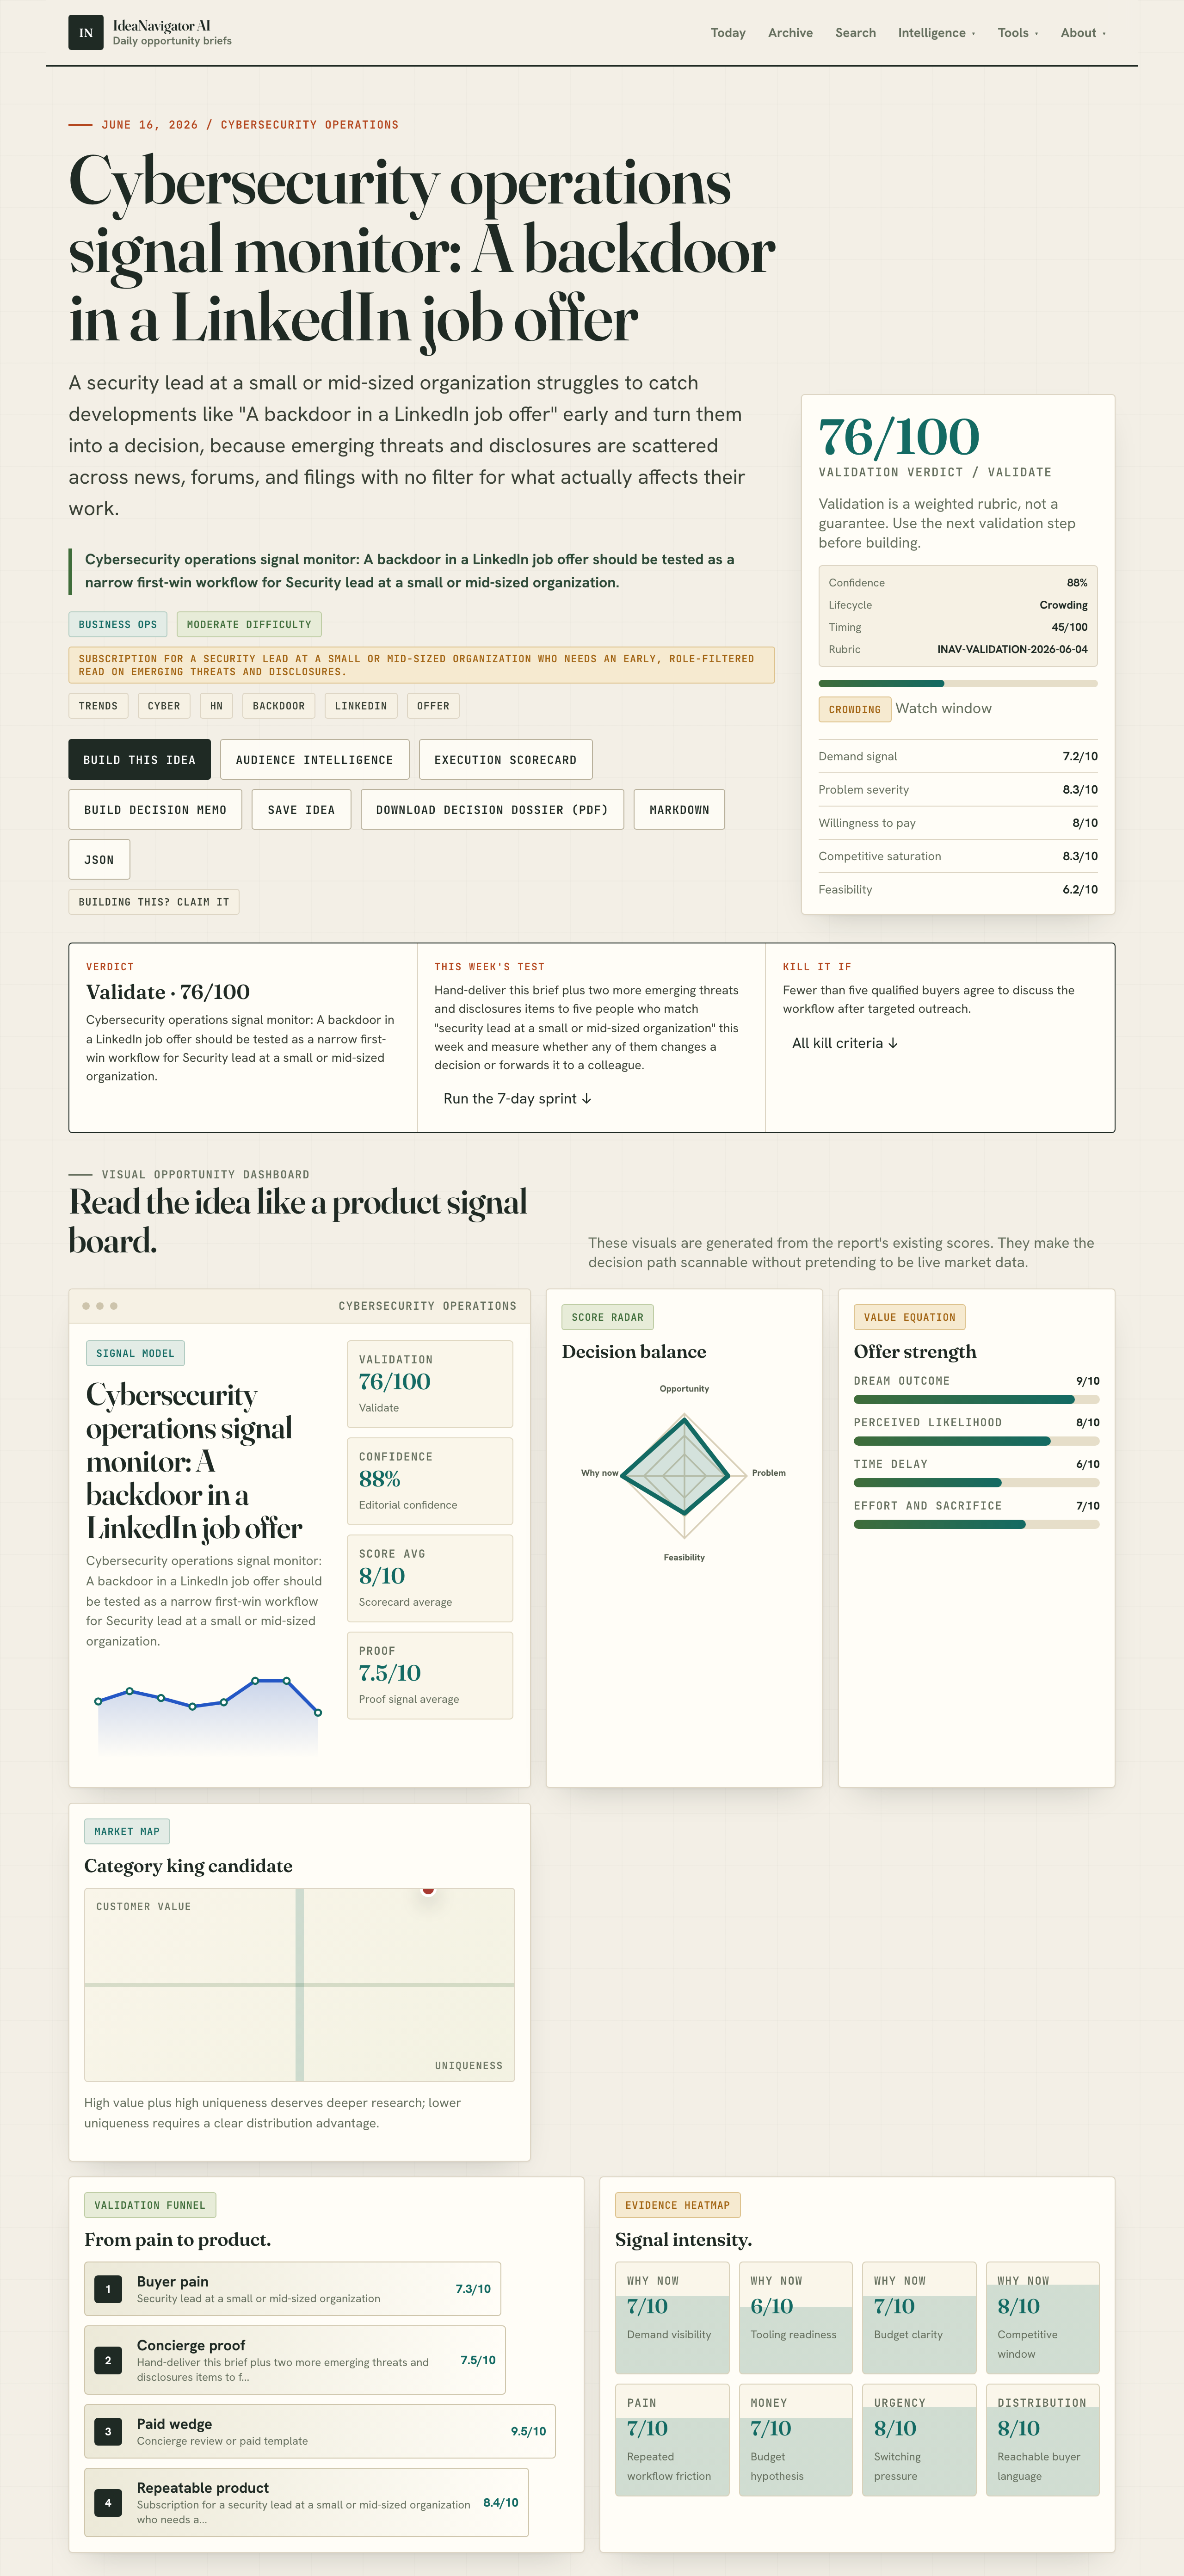
📊 Full opportunity report: Cybersecurity operations signal monitor: A backdoor in a LinkedIn job offer on IdeaNavigator AI — validation score, market gap, and execution plan.

Get hardware and tech essentials delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
TL;DR
Cybersecurity monitoring has confirmed the presence of a backdoor in a LinkedIn job offer. This development highlights emerging threats targeting organizations via social engineering. The event underscores the need for vigilant threat detection.
Cybersecurity operations have confirmed the existence of a backdoor embedded in a LinkedIn job offer, representing a potential security threat. The discovery was made through active monitoring of emerging threat signals, emphasizing the importance of role-specific threat detection for small and mid-sized organizations.
The backdoor was identified during routine cybersecurity signal monitoring, specifically through analysis of social engineering tactics used in job postings on LinkedIn. Experts indicate that malicious actors may use such backdoors to gain unauthorized access to organizational networks. The threat was flagged by cybersecurity teams observing suspicious activity linked to a particular job listing, which appeared to contain malicious code or links designed to compromise targeted systems. At this stage, authorities have not disclosed detailed technical findings or attribution, and investigations are ongoing. Organizations are advised to scrutinize similar postings and maintain heightened vigilance against social engineering vectors.Implications for Organizational Cyber Defense
This incident underscores the increasing sophistication of cyber threats exploiting social engineering via professional networks. For small and mid-sized organizations, such backdoors represent a serious risk, potentially allowing attackers to infiltrate internal systems undetected. The detection highlights the importance of targeted threat monitoring and proactive security measures. As threat actors refine their tactics, organizations must update their security protocols to identify and mitigate similar vulnerabilities quickly. Early detection, as demonstrated here, can prevent significant breaches and data loss, making this a critical development for cybersecurity teams.cybersecurity threat detection software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Over the past year, cybercriminals have increasingly used social engineering tactics on platforms like LinkedIn to target organizations. These tactics include embedding malicious code in job offers, fake recruiter profiles, and phishing links designed to lure security-conscious employees into clicking malicious links. The rise of such threats has prompted cybersecurity professionals to develop more sophisticated signal monitoring tools, capable of filtering relevant threats from the vast volume of online activity. The recent discovery of a backdoor in a LinkedIn job offer is part of this broader trend, illustrating the evolving landscape of targeted cyber threats and the importance of role-specific threat intelligence.
“Detecting a backdoor in a LinkedIn job offer demonstrates how threat actors are increasingly leveraging social engineering to bypass traditional defenses.”
— an anonymous cybersecurity expert
social engineering detection tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Technical Details and Attribution Still Unclear
It is not yet clear who is behind the backdoor or the full technical details of the compromise. Authorities are still investigating whether this is part of a broader campaign or a targeted attack on specific organizations. The scope of affected organizations and the potential impact remain to be determined as more information becomes available.network security monitoring devices
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Next Steps in Investigation and Defense Measures
Authorities and cybersecurity teams will continue investigating the origin and scope of the backdoor. Organizations are advised to review their social engineering defenses, scrutinize similar job postings, and implement enhanced monitoring for suspicious activity. Further technical details and attribution are expected to emerge in the coming weeks, which will inform targeted defensive strategies. Monitoring tools may be updated to better detect such threats in real-time.As an affiliate, we earn on qualifying purchases.
Key Questions
How was the backdoor in the LinkedIn job offer detected?
The backdoor was identified through active cybersecurity signal monitoring, which flagged suspicious activity linked to a specific job posting containing malicious code or links.
Who is likely behind this threat?
Attribution is still under investigation; authorities have not confirmed the identity or group responsible for the backdoor.
What should organizations do to protect themselves?
Organizations should scrutinize job postings on social platforms, enhance their social engineering defenses, and monitor for suspicious activity related to recruitment and hiring processes.
Is this a widespread threat or targeted attack?
It is currently unclear whether this is a targeted attack against specific organizations or part of a broader campaign exploiting social engineering tactics.
When will more details be available?
Further technical details and attribution are expected to be released as investigations progress over the coming weeks.
Source: IdeaNavigator AI
Evergreen bestsellers Picks
bestsellers
As an affiliate, we earn on qualifying purchases.