📊 Full opportunity report: Why SMB Endpoint Security Matters For Remote Teams With Diverse Devices on IdeaNavigator AI — validation score, market gap, and execution plan.
Get ready for Prime Big Deal Days — try Prime free
Exclusive member deals on October 6–7, plus fast free delivery. Cancel anytime.
Start your free trialAs an affiliate, we earn on qualifying purchases.
TL;DR
A new device security checker for remote SMB teams helps verify device compliance across mixed hardware without invasive MDM. It addresses a growing security gap due to employee-owned devices and compliance needs.
Remote SMB teams using a variety of personal and unmanaged devices face increasing security and compliance challenges, prompting the development of a lightweight device security checker. This tool, currently being tested at several startups, aims to verify device encryption, OS updates, and screen lock status without invasive management, providing a scalable solution for organizations with diverse hardware.
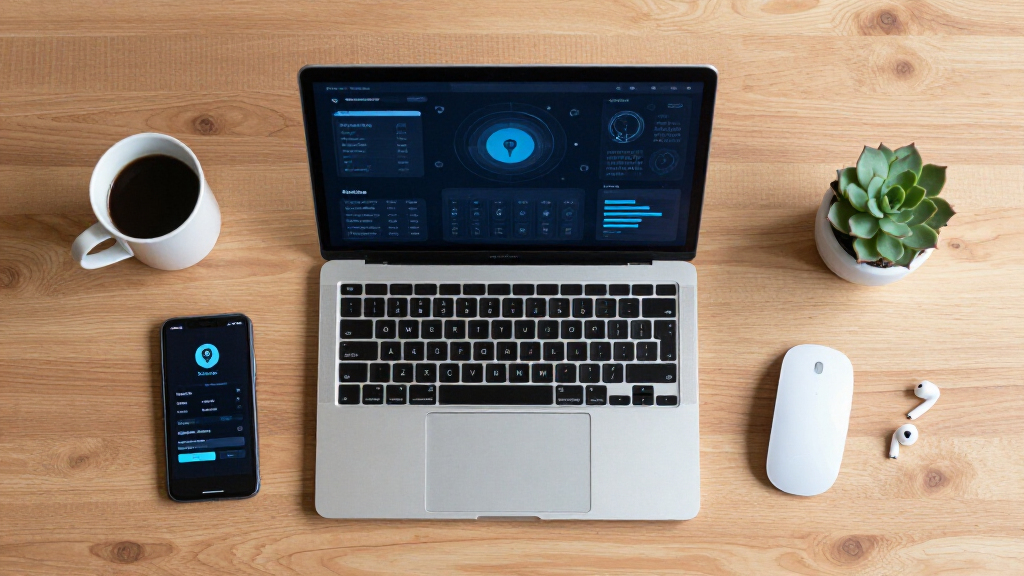
The device security checker is a minimal, voluntary agent that employees install on their personal devices, including MacBooks, Windows laptops, and smartphones. It checks critical security parameters such as disk encryption, OS updates, screen lock activation, and password manager presence. The results are reported to a team dashboard, which offers self-remediation instructions if devices fail compliance checks.
This approach responds to the growing demand for SMBs to meet compliance standards like SOC 2, especially as traditional Mobile Device Management (MDM) solutions are often too invasive or impractical for employee-owned hardware. The initial deployment involves ten remote startups, with the goal of measuring device enrollment rates and assessing whether auditors accept the generated compliance reports as sufficient evidence of security posture.
Pricing is structured per device on a monthly basis, with additional features such as compliance report exports available on paid tiers. The solution emphasizes simplicity and voluntary participation, aiming to fill a verification gap left by existing management tools that struggle to balance security with employee privacy and convenience.
Why SMBs Need Lightweight Endpoint Verification
As remote work becomes standard, small and medium-sized businesses (SMBs) face increasing pressure to ensure their devices are secure and compliant with industry standards. The new device checker targets a critical gap in endpoint security for organizations relying on employee-owned, mixed-OS hardware. Traditional management tools like MDM are often seen as too invasive, leading to low adoption or resistance from employees.
By offering a lightweight, voluntary solution, SMBs can verify device security posture efficiently, reducing the risk of data breaches and compliance violations. This is especially relevant as regulatory frameworks like SOC 2 tighten their requirements and auditors demand more concrete evidence of endpoint security. The tool’s ability to provide clear, reportable security status without remote control or invasive management makes it a practical option for SMBs navigating the complexities of remote work security.
device encryption verification tool
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Growing Security Challenges in Remote SMB Environments
The shift to remote work has led many SMBs to rely heavily on employee-owned devices for accessing company data and applications. This creates a fragmented security landscape, where IT teams often lack visibility into device security status. Many devices—ranging from aging Windows laptops to personal MacBooks and unmanaged smartphones—may lack essential protections such as disk encryption, timely OS updates, or active screen locks.
Historically, organizations have used Mobile Device Management (MDM) solutions to enforce security policies, but these are often too invasive for personal devices and can face resistance from employees. As a result, many SMBs operate with a verification gap, where they cannot confidently demonstrate that devices meet security standards during audits or in response to security incidents.
Recent regulatory pressures, such as SOC 2 audits, have increased the urgency for SMBs to adopt scalable, non-intrusive verification methods. The development of lightweight, agent-based checkers aims to address this gap, providing a practical way to verify compliance without overstepping employee privacy boundaries.
As an affiliate, we earn on qualifying purchases.
Uncertainties About Adoption and Regulatory Acceptance
It is still unclear how widely SMBs will adopt this new device checker and whether regulatory bodies and auditors will accept its reports as sufficient evidence of security compliance. The initial deployment at ten startups aims to gather data on enrollment rates and audit acceptance, but broader validation remains pending.
Additionally, questions remain about the tool’s effectiveness across different device types, operating systems, and organizational policies. The long-term impact on device security posture and employee privacy will also need ongoing assessment as the solution scales.
As an affiliate, we earn on qualifying purchases.
Next Steps for Deployment and Validation
The pilot program at ten remote startups will continue to collect data on device enrollment, compliance report acceptance, and user feedback. If successful, the company plans to expand deployment to a larger cohort of SMBs and refine the agent’s capabilities based on initial findings.
Further validation with security auditors and regulatory bodies will be essential to establish the tool’s credibility. The company also intends to develop integrations with existing security and compliance workflows, making it easier for SMBs to incorporate the checker into their broader security strategies.
As an affiliate, we earn on qualifying purchases.
Key Questions
How does the device security checker work?
The checker is a lightweight agent that employees voluntarily install on their personal devices. It verifies security features such as disk encryption, OS updates, screen lock activation, and password manager presence, reporting results to a dashboard.
Will this replace traditional MDM solutions?
No, the tool is designed as a lightweight, non-invasive supplement for verification purposes, especially suitable for employee-owned devices where MDM is impractical or resisted.
Is this solution compliant with privacy regulations?
The tool focuses on security posture checks without remote control or data collection beyond verification results, aiming to respect employee privacy while meeting compliance needs.
When will this be generally available?
The current deployment is in pilot stage; broader availability depends on pilot outcomes and regulatory acceptance, which are still being evaluated.
How much does it cost?
The pricing is per device on a monthly basis, with additional features such as compliance report exports available on paid tiers.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.